Hacking Google
Google posted a series called Hacking Google and it was pretty interesting. I wanted to share it with everyone.
There’s quite a few (9) of these short videos.

Google posted a series called Hacking Google and it was pretty interesting. I wanted to share it with everyone.
There’s quite a few (9) of these short videos.
Recover isn’t about disaster recovery, its about restoring business to an acceptable operating state and if we learned enough to become resilient. You’re on the final part, Recover, of my series on Building a Metrics Program using the CSF. I wrote about Govern, Identify, Protect, Detect, and Respond prior to this page, leveraging the CSF…
Another program near to me as I took over the SOC. The NIST and the CSF guided me in the ways of incident response… that and my kick-ass team who built the program with me. Without a doubt, since you are on part 5 of 6, I feel you are prepared to read more, but…
Detect directly influenced a program that I helped stand up when I was given a SOC to lead. Honestly, I really enjoyed it. It inspired me to write about it. Since you’re on part 4 of 6, I assume you’ve read about Govern, Identify, and Protect and are following on to see how deep this…
Protect should answer: Are the controls we have in place actually reducing the risks we’ve identified? You should be able to see the pattern now that as we move through these parts, that the Cyber Defense Matrix lesson comes into play. We are walking from left to right in a security sense, or from a…
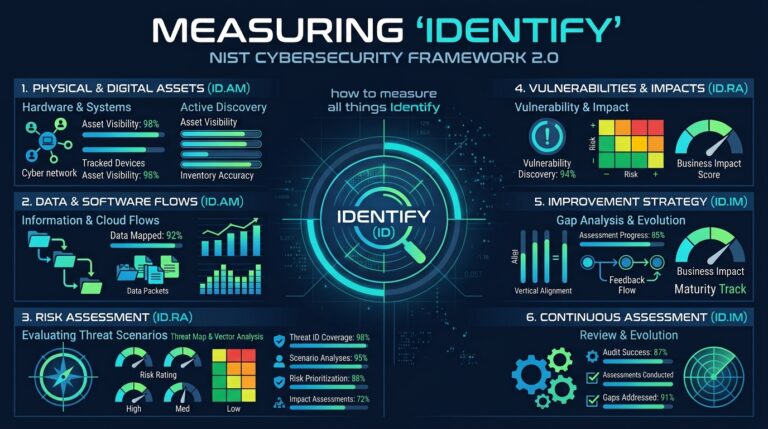
This is a continuation of my CSF Actionable Metrics series. If you missed the first one, here’s the link to it. So with identify, its about Asset Management, Risk Assessments, and Improvement. This is part of my bigger series of Building a Metrics Program. Identify within the CSF is about knowing your inventory, just like…

I’m a huge fan of metrics, over the many years I’ve been doing cybersecurity, I’ve been able to prove the progress of my own work to proving the progress of my departments. From individual contributor to leader. One of the things I really like about the Cybersecurity Framework, is that its short and sweet and…